الأمن السيبراني· CYBERSECURITY · AI RED-TEAMING
Khasmخصم
The adversary you choose, testing every AI system before a real one does.
A continuous AI red-teaming platform that attacks your own LLM copilots, chatbots, and agentic AI systems — prompt injection, jailbreaks, data leakage, and tool misuse — turning a one-time AI safety review into a running findings register.
من يختبر ذكاءه الاصطناعي أولًا لا يُفاجأ بثغراته
“Whoever tests their own AI first is never surprised by its flaws.”
What Khasm does
Prompt-injection & jailbreak attack library
Continuously updated adversarial prompt suites test every LLM-backed copilot and chatbot against the latest bypass techniques.
Agentic tool-misuse testing
For agents with tool or function-calling access, tests whether the agent can be coaxed into an unauthorized or destructive action, not just a bad text output.
Data-leakage & exfiltration probes
Tests whether a system can be tricked into revealing its system prompt, another user’s data, or restricted context.
Findings register with proof
Every successful attack is captured as a reproducible transcript, so remediation teams fix the real failure instead of guessing at a score.
Remediation SLAs & re-test
Critical and high findings carry a fix-by clock, with re-test scheduled automatically after a fix.
Sovereign hosting
Attack transcripts and model outputs — some of your most sensitive AI behavior data — never leave the Kingdom.
See Khasm in action
An early UX walkthrough of the product, designed bilingually from day one.
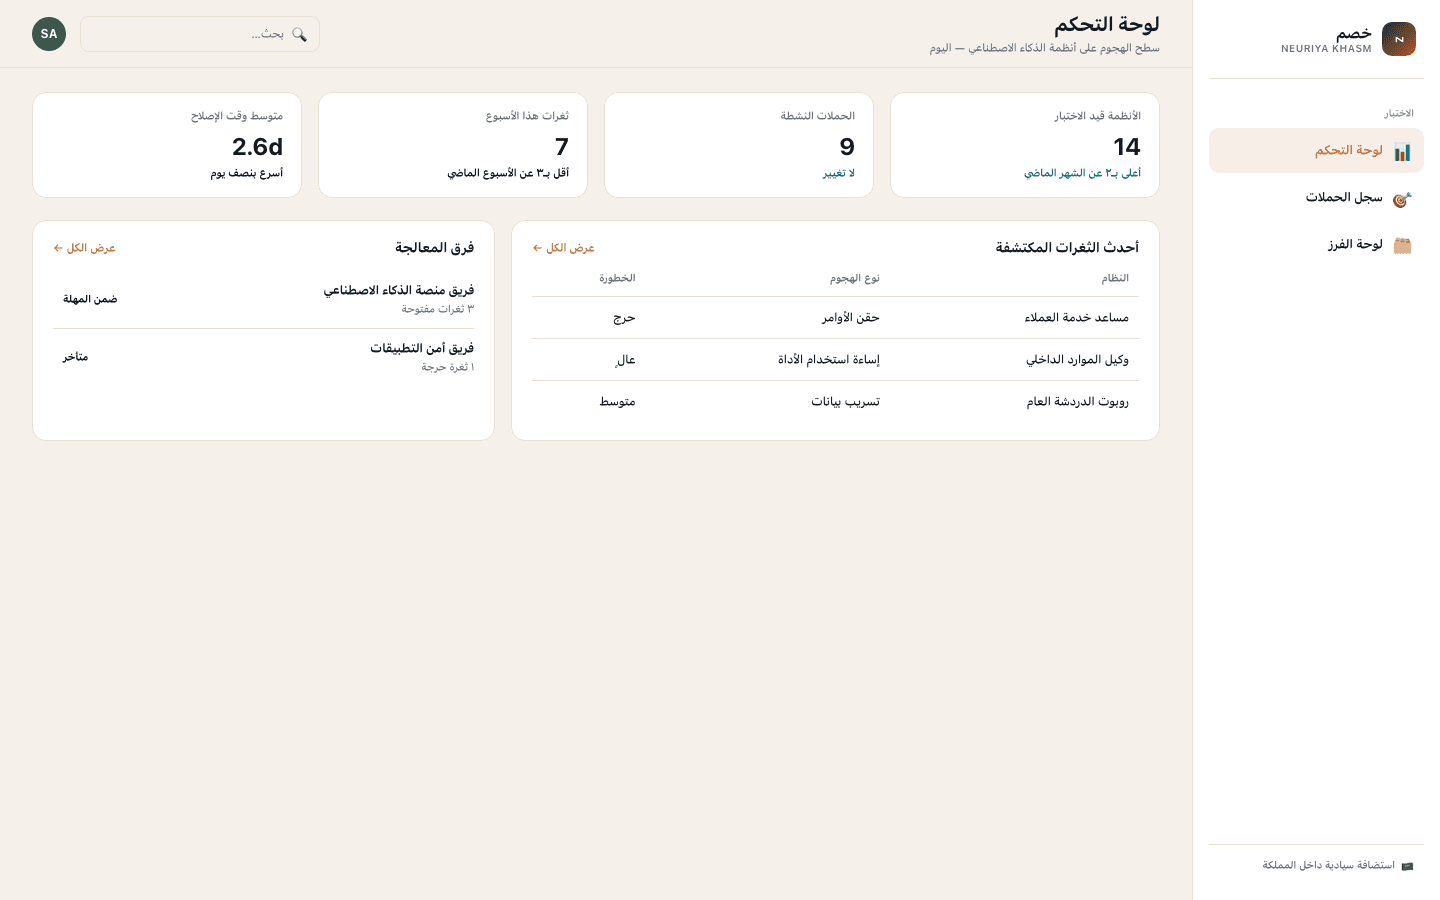
AI attack-surface dashboard
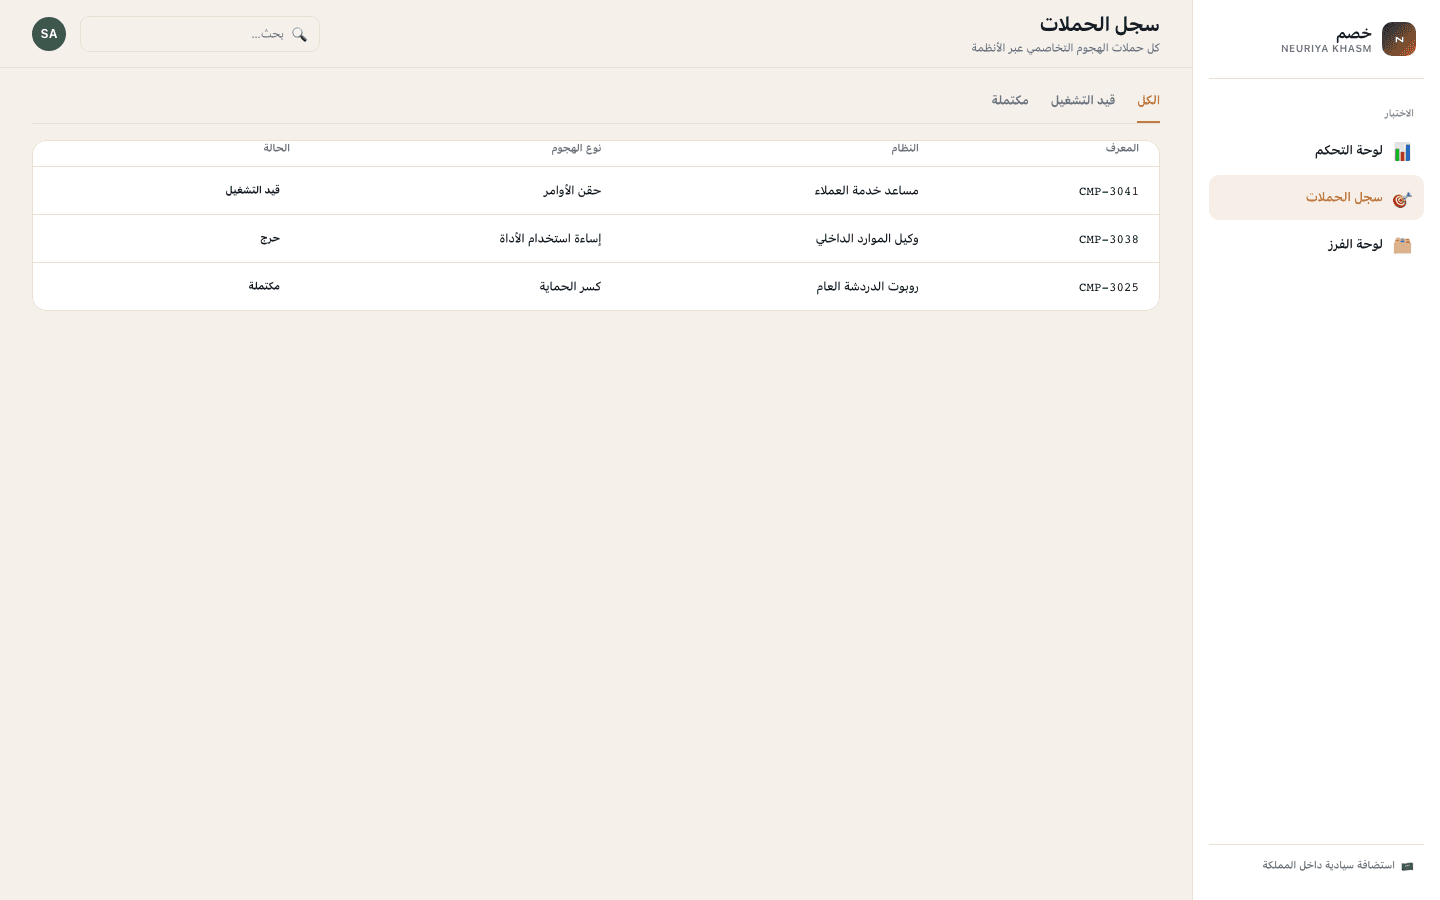
Attack campaign log
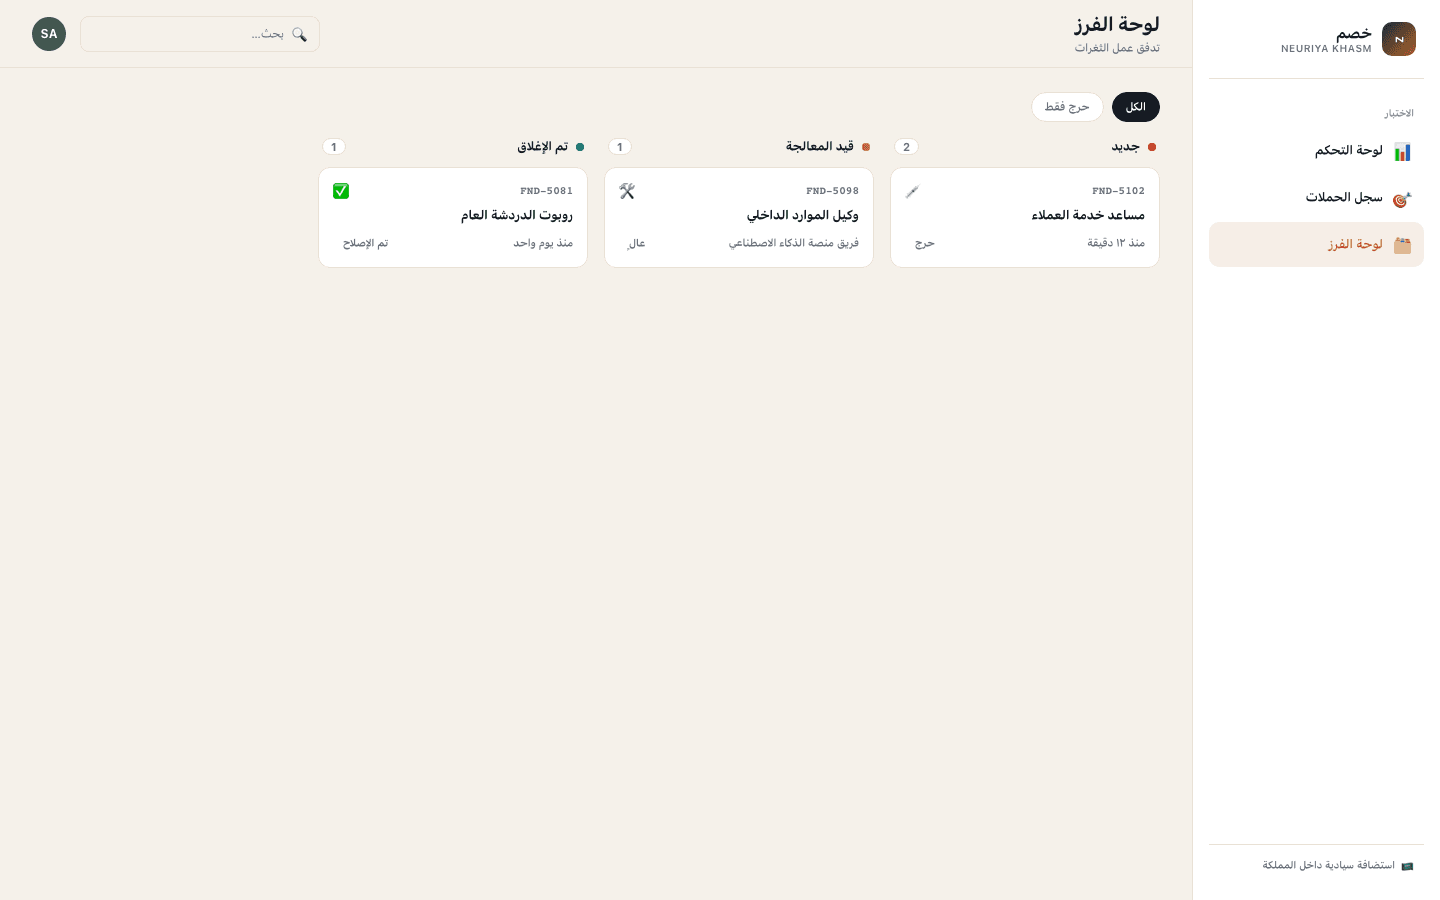
Findings triage board
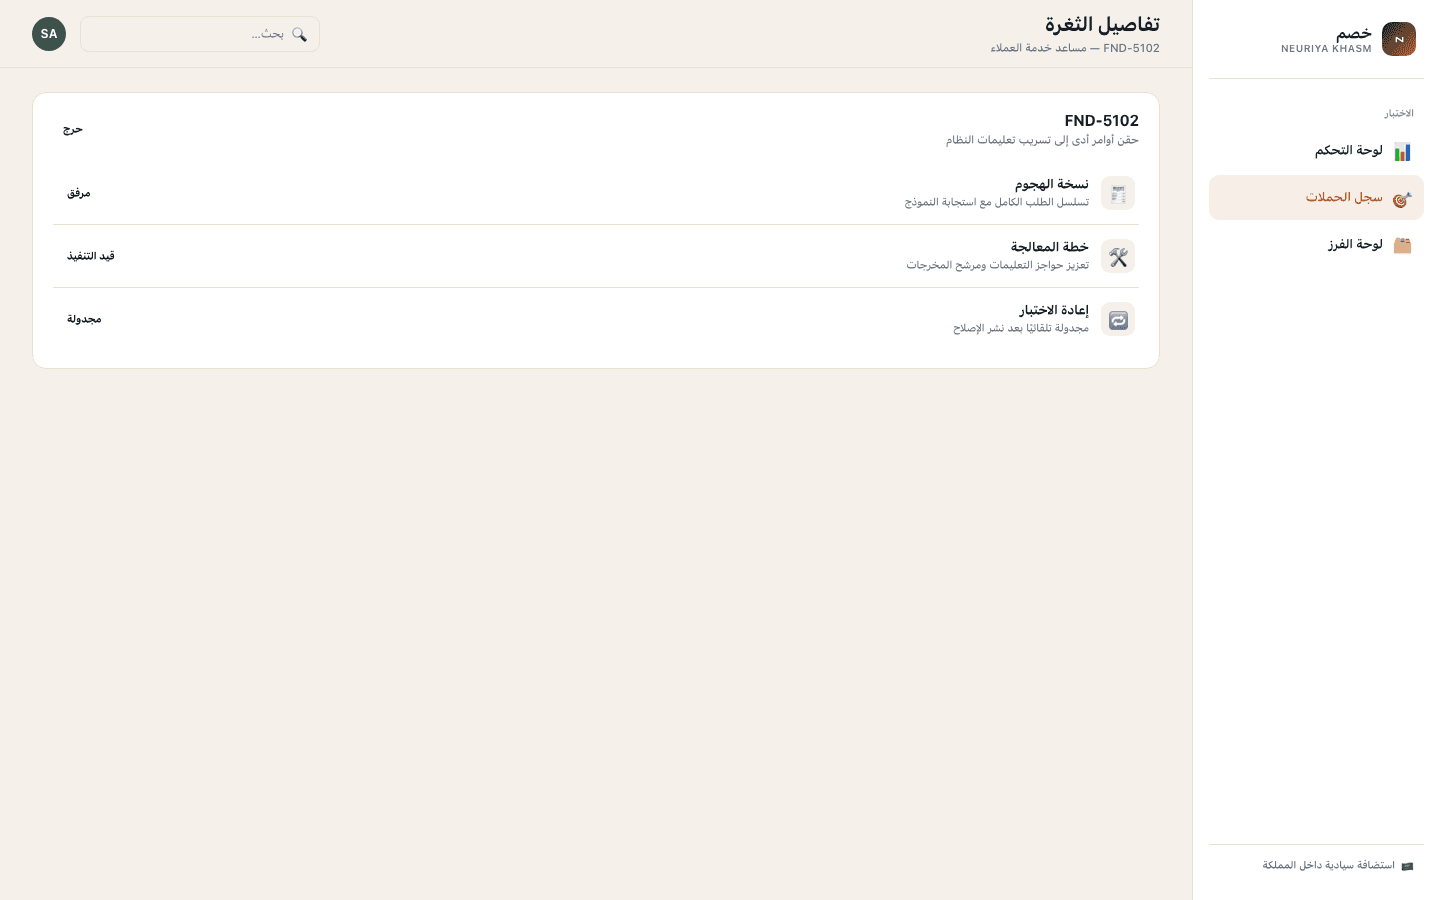
Finding transcript detail
How it works
Scope
Register the LLM apps, copilots, and agents in scope, along with their tool and data access.
Attack
Automated adversarial campaigns run continuously against each system, no engagement scheduling required.
Triage
Every successful bypass logged as a finding with its full transcript and severity.
Remediate & re-test
Findings route to owning teams with an SLA clock; a fix triggers an automatic re-test before closure.
Make AI red-teaming a habit, not an audit
We're selecting design-partner teams running LLM copilots or agentic AI in production for the first pilot cohort. Book a briefing to see the product and discuss fit.
Request a Pilot