الأمن السيبراني· CYBERSECURITY
Harisحارس
24/7 in-Kingdom detection and response, without building your own SOC.
A managed SOC and MDR service giving mid-market and enterprise teams around-the-clock threat detection, triage, and incident response — hosted and staffed inside the Kingdom.
من راقب الليل أمن الصباح
“Whoever watches the night secures the morning.”
What Haris does
In-Kingdom 24×7 monitoring
A sovereign SOC watching your estate around the clock, with analysts based inside the Kingdom.
Threat hunting, not just alerting
Proactive hunts across your environment, not just a queue of unreviewed alerts.
Full incident lifecycle
Detection, containment, compliance notification, and final report — tracked on every incident.
On-call escalation built in
A named on-call team with clear handoffs, so a critical incident never waits for a shift change.
Asset-aware coverage
Coverage mapped to your actual asset inventory, with gaps surfaced instead of assumed.
NCA-aligned reporting
Incident reports formatted for NCA and sector-regulator notification timelines.
See Haris in action
An early UX walkthrough of the product, designed bilingually from day one.
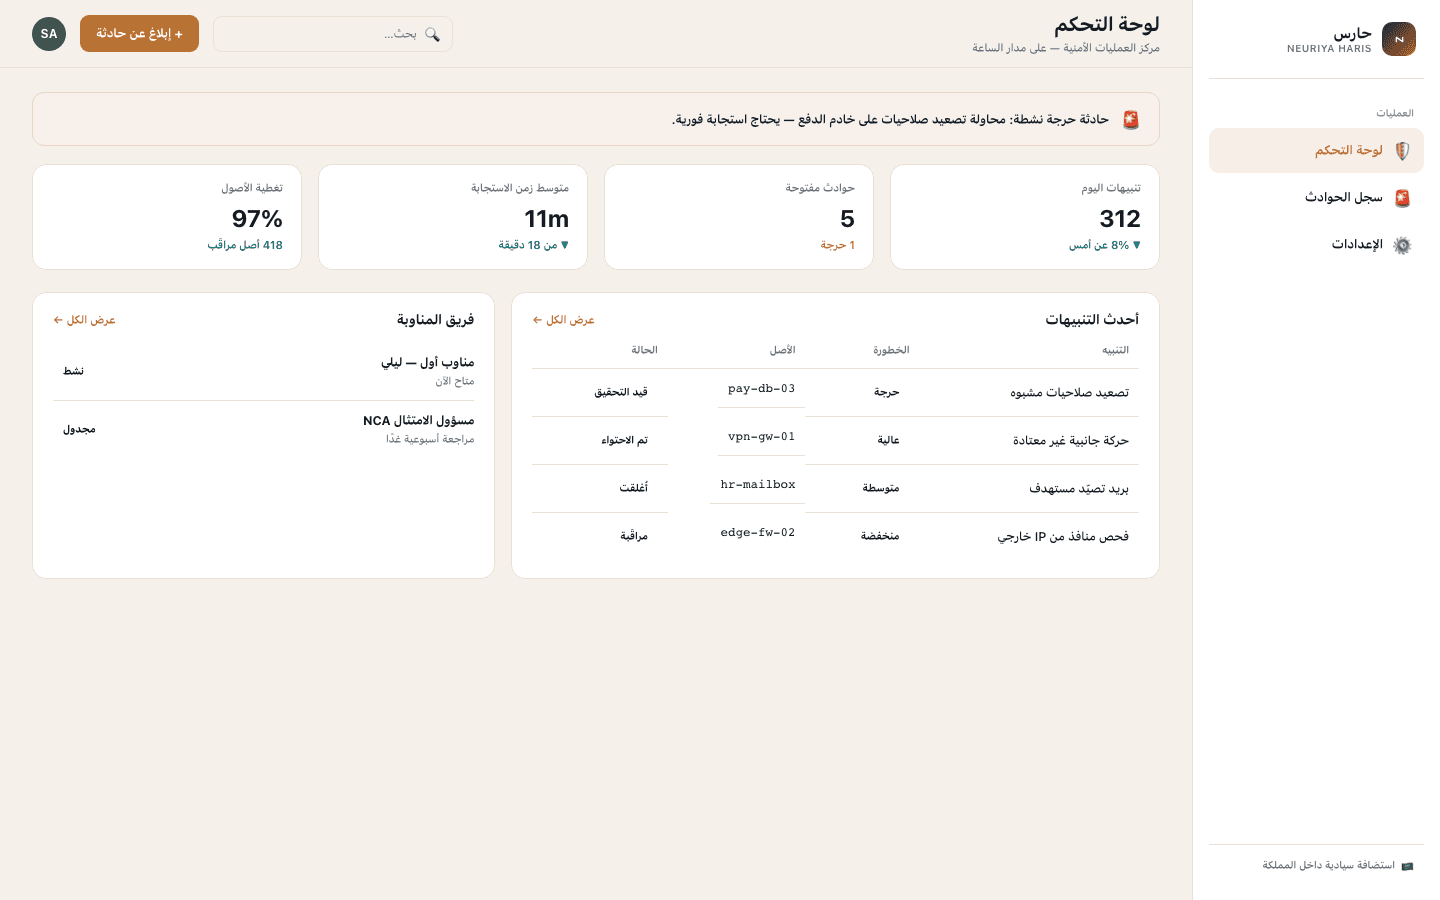
SOC dashboard
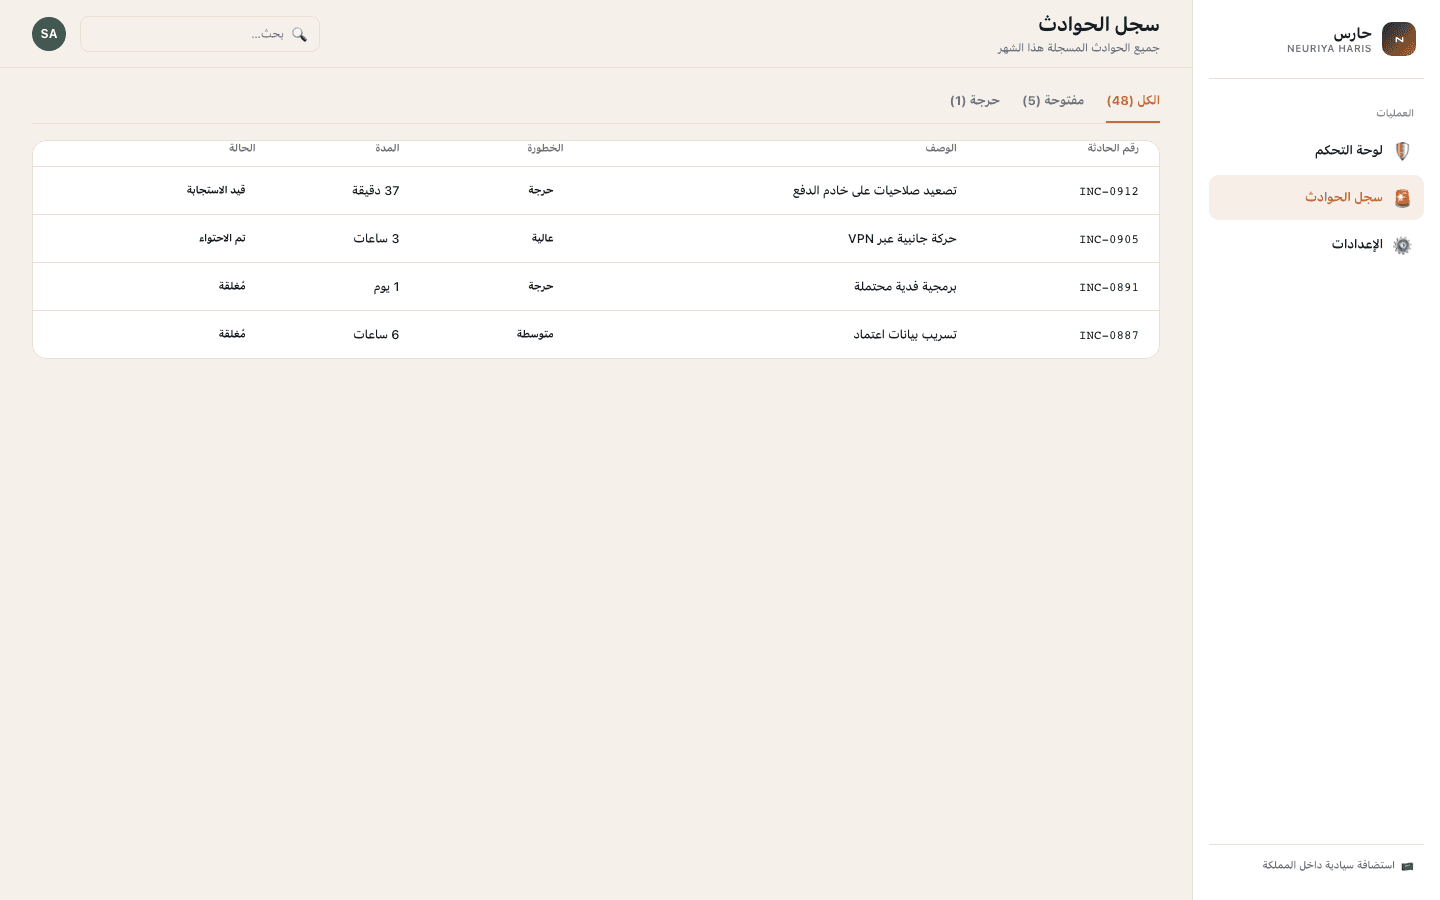
Incident log
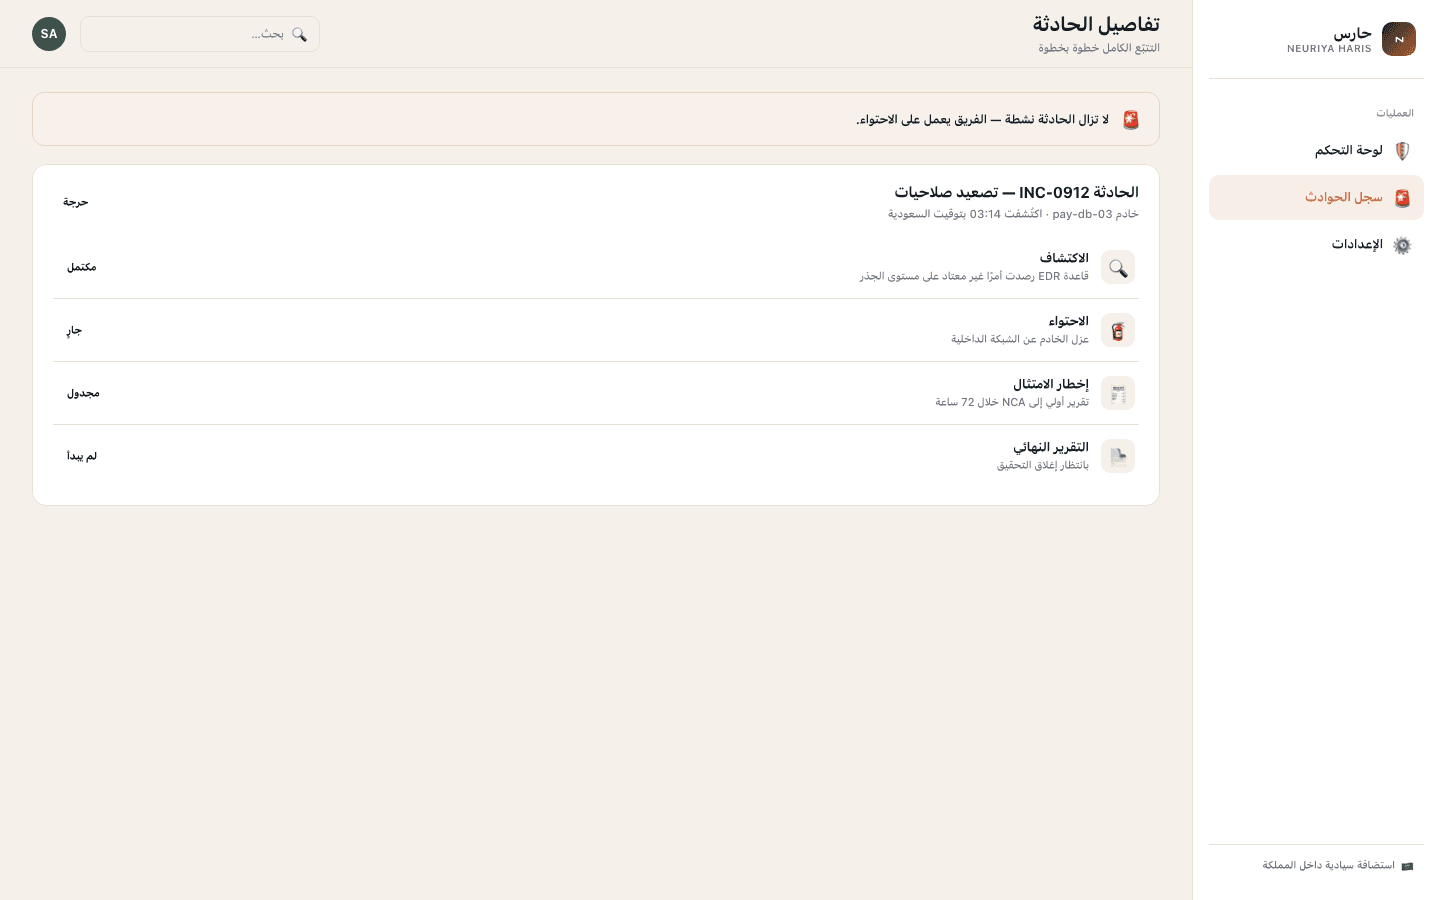
Incident detail
How it works
Connect your estate
Log sources, EDR, and network telemetry connect into the SOC within days, not months.
Detect
Around-the-clock monitoring flags anomalies against tuned, environment-specific rules.
Respond
Analysts contain and remediate, with every action logged against the incident.
Report
A compliance-ready report closes the loop for your board and your regulator.
Stop building a SOC you can’t staff
We're selecting design-partner enterprises for the first pilot cohort. Book a briefing to see the product and discuss fit.
Request a Pilot