الأمن السيبراني· CYBERSECURITY
Redlineاختبار الاختراق
Continuous, threat-led penetration testing aligned to SAMA’s FEER programme.
A platform for continuous pen-testing, web/API/mobile security testing, and threat-led red teaming — turning point-in-time engagements into a running findings register.
من يختبر دفاعه أولًا لا يُفاجأ بعدوه
“Whoever tests their own defences first is never surprised by an adversary.”
What Redline does
Continuous engagement tracking
Every web, API, mobile, and network engagement tracked in one place, not scattered PDFs.
Findings register with proof
Every finding carries its proof of concept, so remediation teams don’t have to reproduce it.
Remediation SLAs
Critical and high findings carry a clock, with re-test scheduled automatically after a fix.
FEER-aligned reporting
Reports formatted for SAMA’s Financial Entities Ethical Red-teaming programme.
Trend visibility for leadership
Time-to-fix and finding-severity trends give CISOs a real posture signal, not just a report count.
Sovereign hosting
Findings and exploit details — some of your most sensitive data — never leave the Kingdom.
See Redline in action
An early UX walkthrough of the product, designed bilingually from day one.
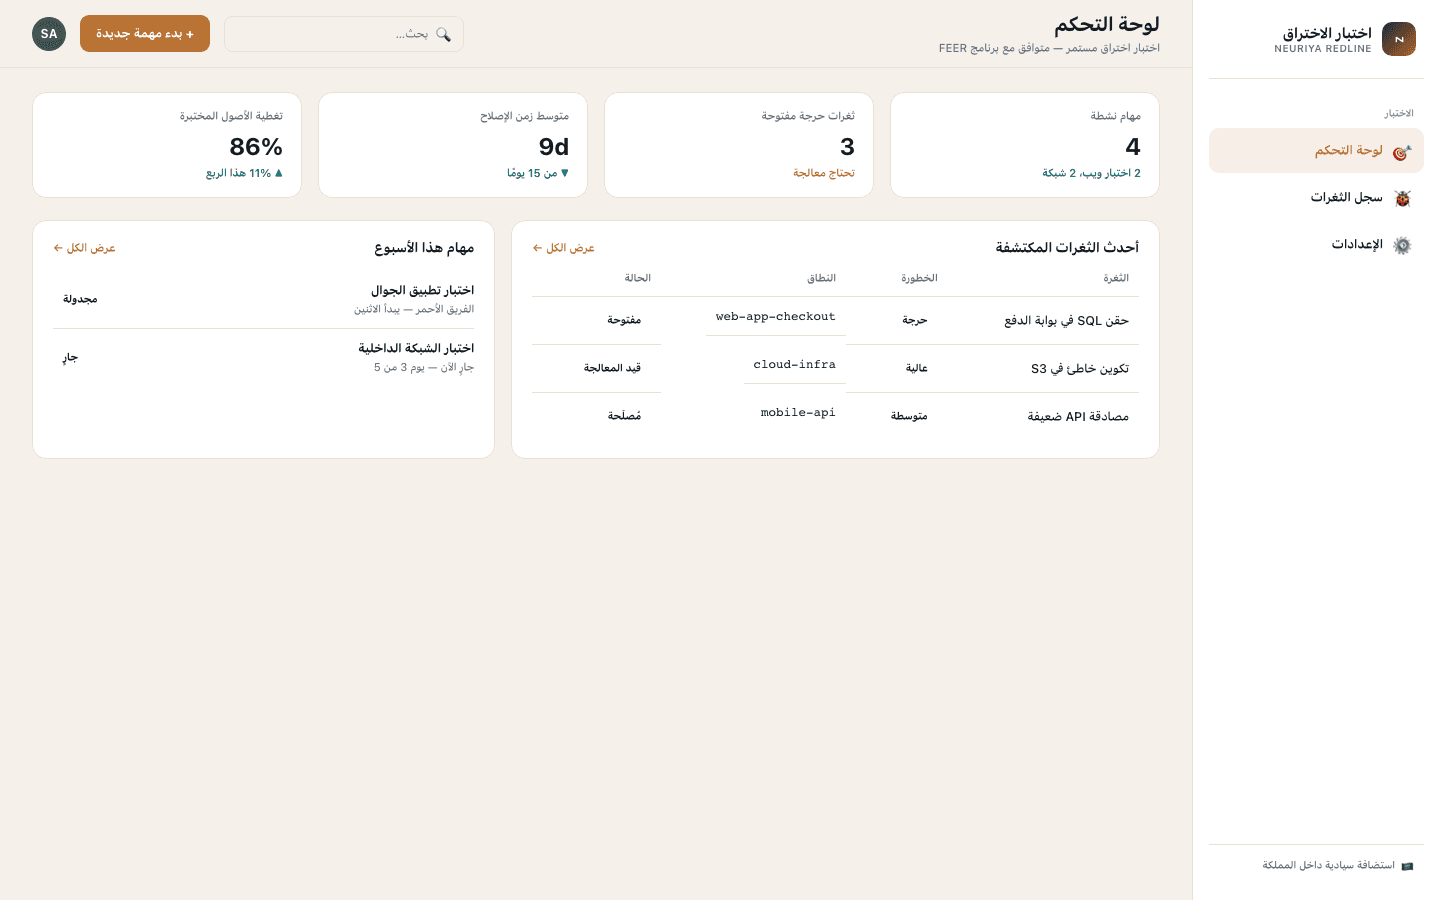
Testing dashboard
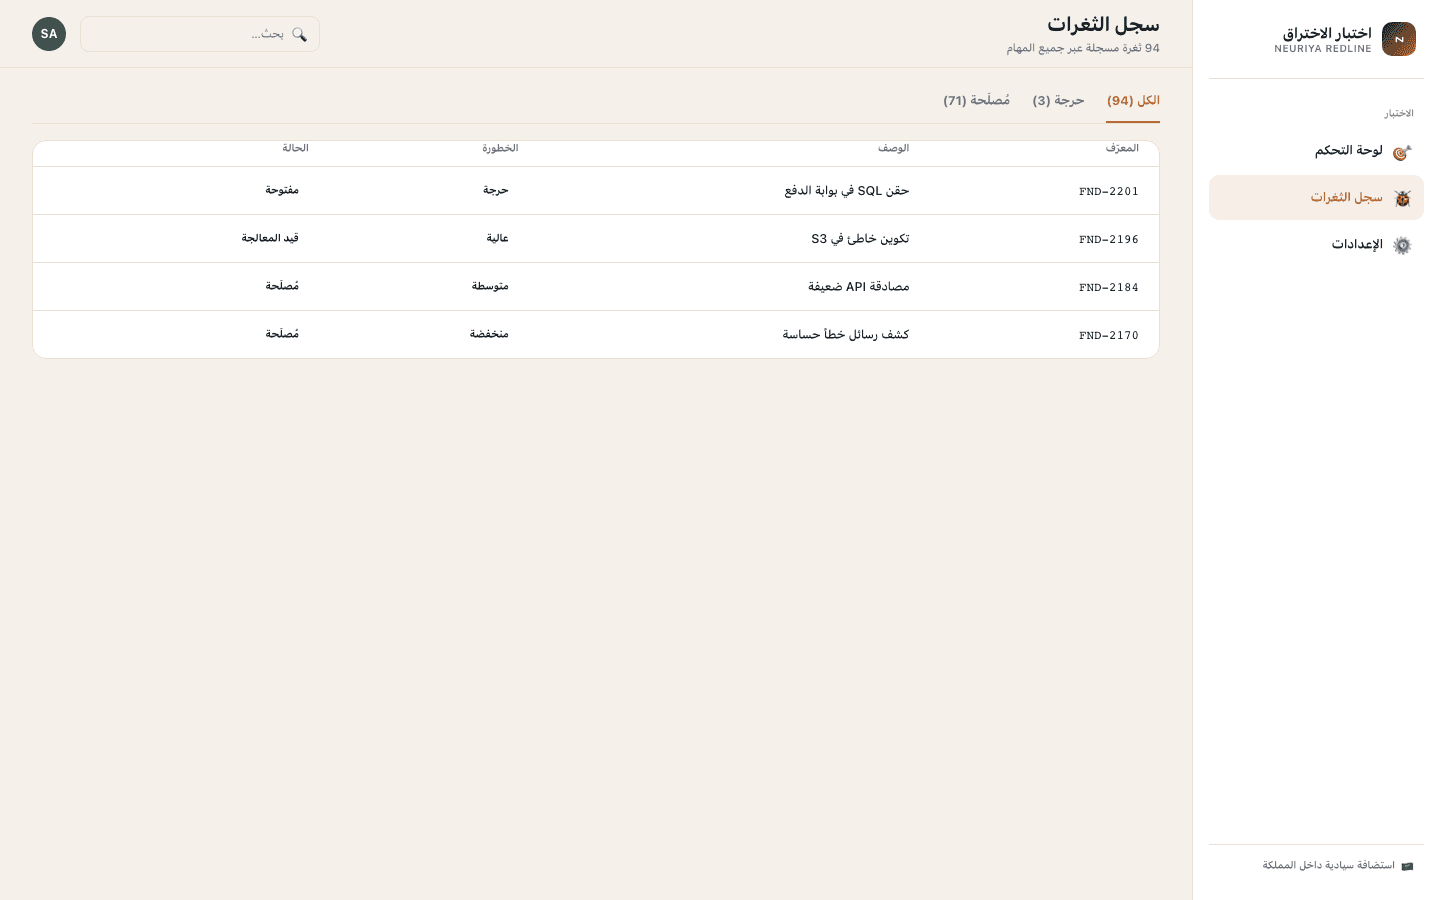
Findings register
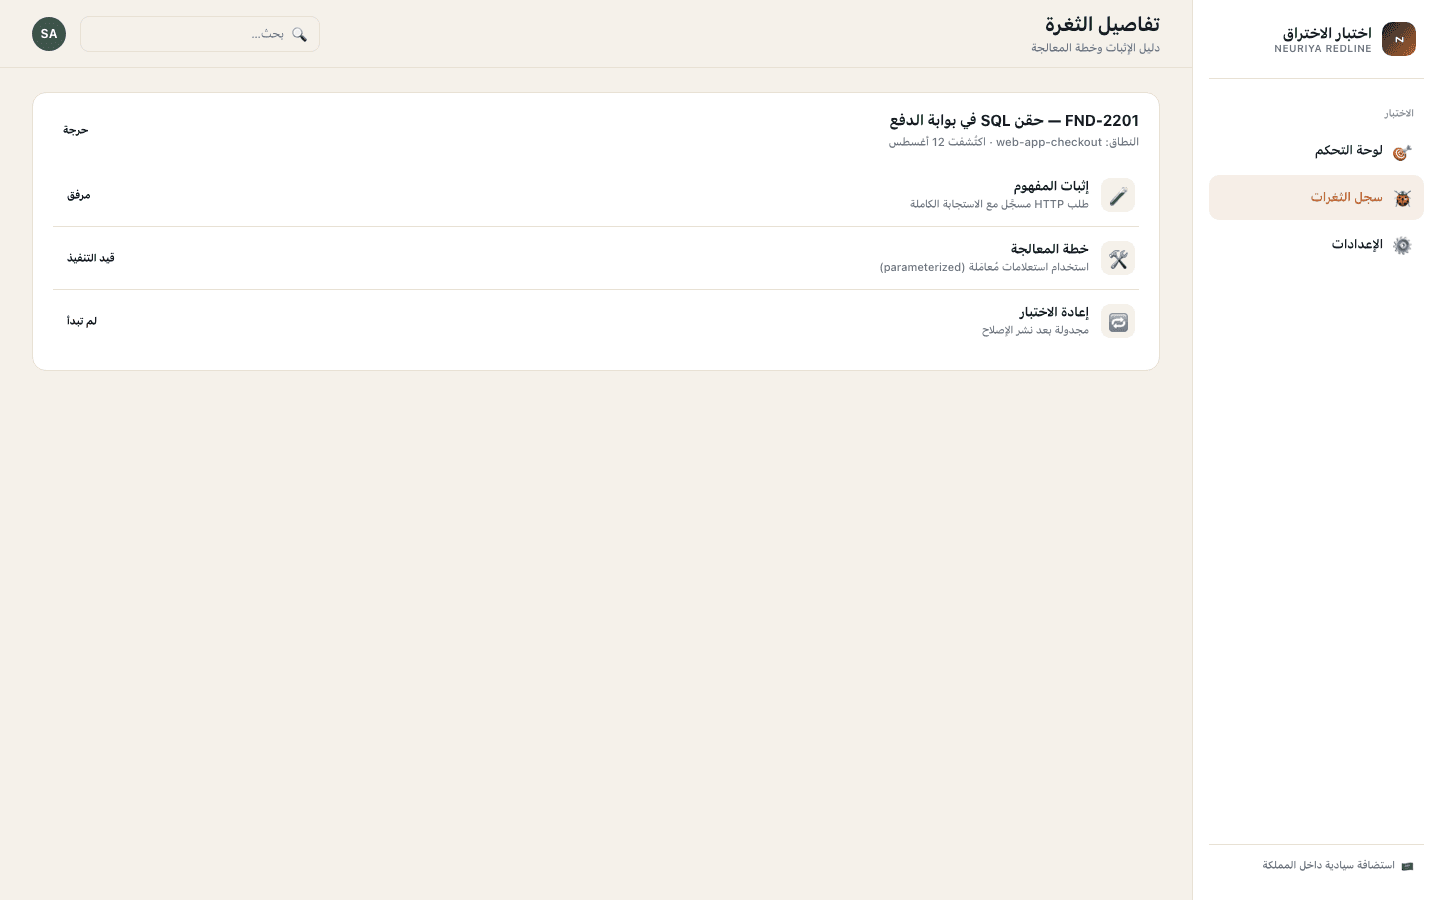
Finding detail
How it works
Scope an engagement
Web, API, mobile, or network — scope and rules of engagement are logged up front.
Test
Testers log findings with proof of concept as they go, not in a report weeks later.
Remediate
Findings route to owning teams with a severity-based SLA clock.
Re-test and close
A fix triggers an automatic re-test before the finding is marked closed.
Make red-teaming a habit, not an event
We're selecting design-partner security teams for the first pilot cohort. Book a briefing to see the product and discuss fit.
Request a Pilot