الدفاع والأمن· DEFENCE & SECURITY · CYBER DEFENCE
Dir'aدرع
Red-team, threat-hunt, and SOC capability tuned for nation-state adversaries.
A cyber-defence capability combining red-team exercises, continuous threat hunting, and SOC operations calibrated for nation-state-level adversaries, built on NCA ECC and CCC controls with classified-domain hardening.
من يعرف عدوّه أولاً، يحتوي التهديد أولاً
“Whoever knows the adversary first, contains the threat first.”
What Dir'a does
Nation-state-calibrated threat hunting
Hunt hypotheses are built around advanced persistent threat tradecraft, not commodity malware signatures.
Continuous red-team exercises
Scheduled adversary simulations against live-representative environments keep defensive posture tested, not assumed.
NCA ECC and CCC control enforcement
Essential and critical cybersecurity controls are tracked and enforced continuously, with remediation status visible at all times.
Classified-domain hardening
Detection and response tooling is built to operate inside classified networks without requiring external telemetry egress.
Incident response with full timeline
Every incident carries a complete response record — detection, isolation, root-cause, control verification, report.
Mean-time-to-contain tracking
Containment performance is measured and trended over time, giving command visibility into actual defensive readiness.
See Dir'a in action
An early UX walkthrough of the product, designed bilingually from day one.
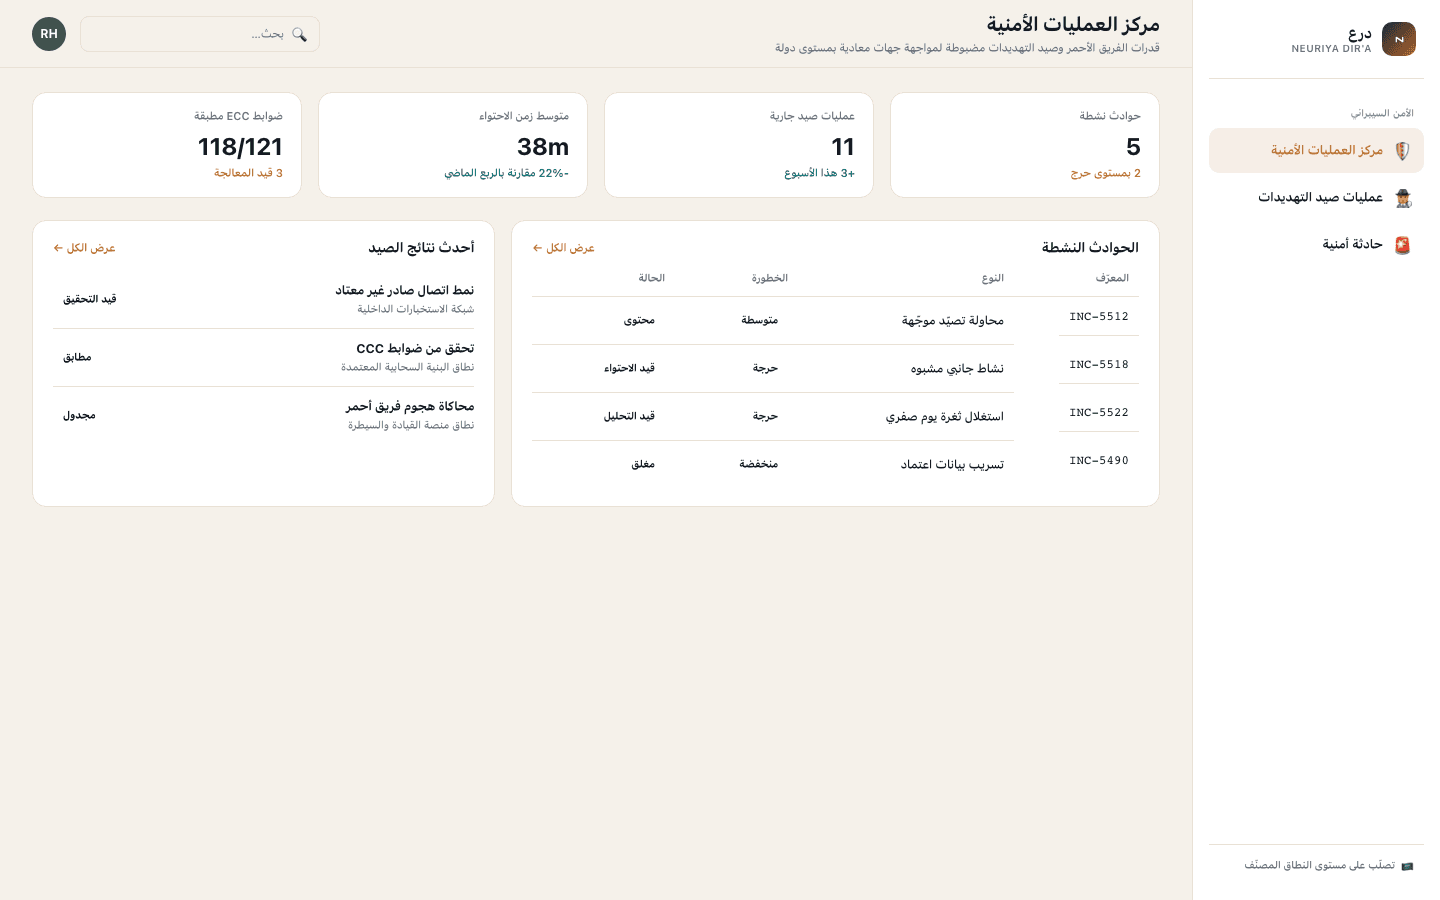
SOC overview
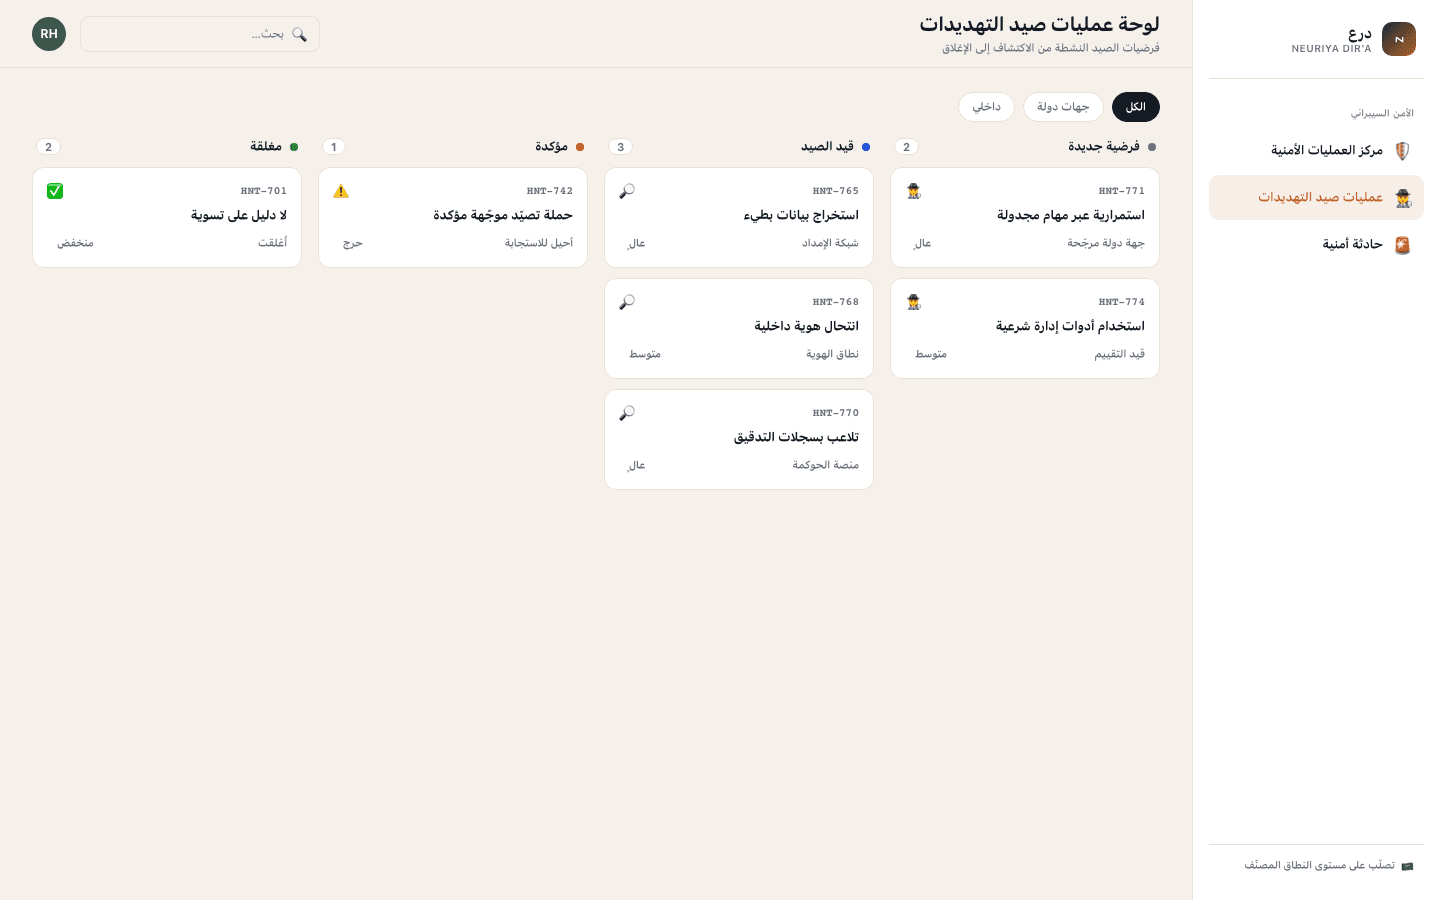
Threat hunt board
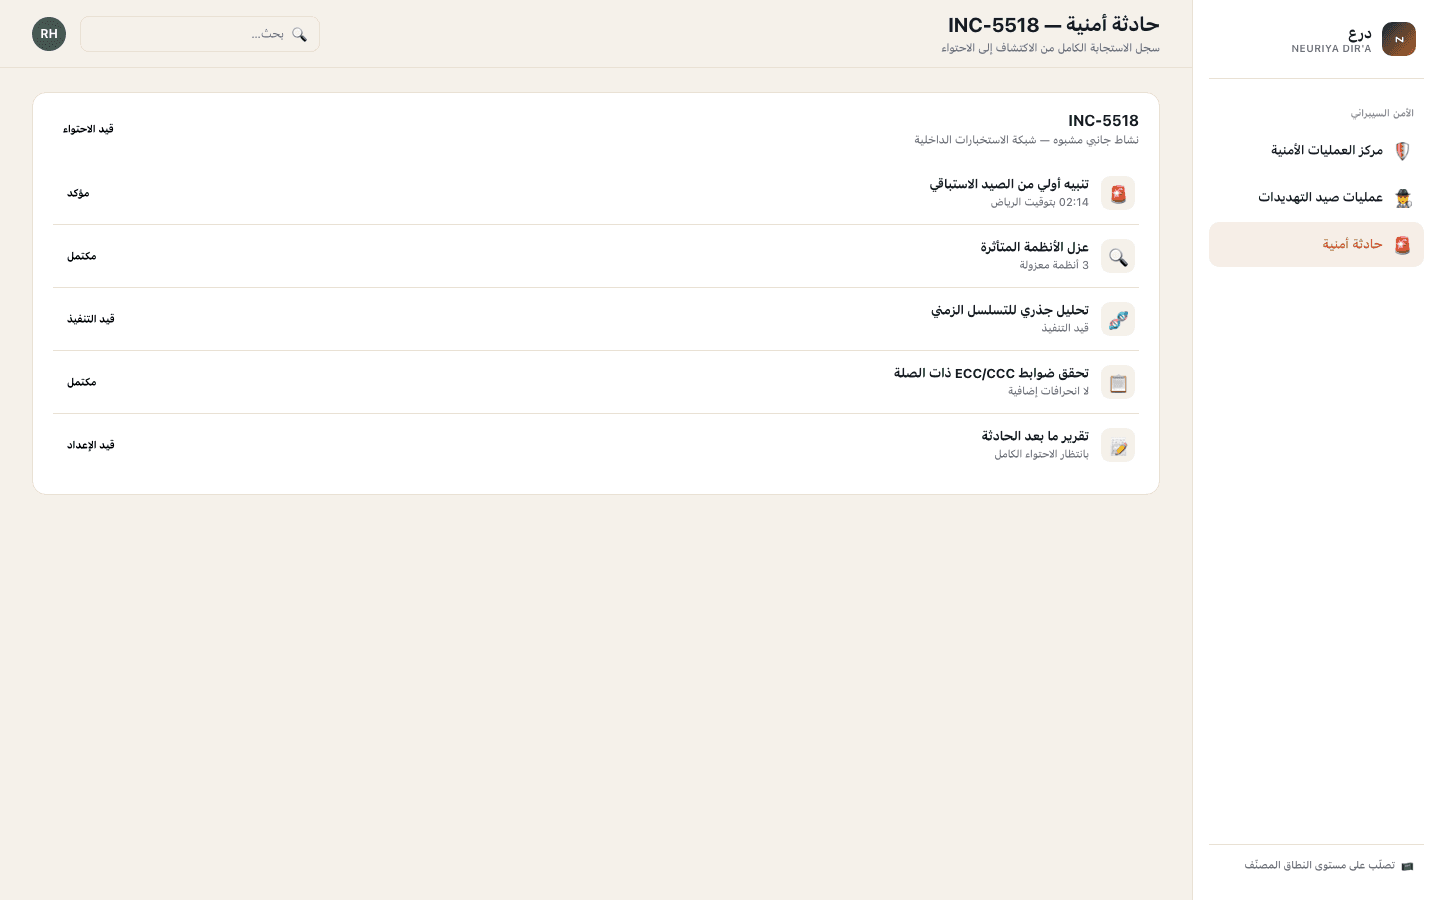
Incident case
How it works
Harden
ECC and CCC controls are baselined and enforced across the classified domain before active defence begins.
Hunt
Threat hunters pursue nation-state-calibrated hypotheses continuously, not only after an alert fires.
Simulate
Scheduled red-team exercises validate that defensive controls hold against realistic adversary tradecraft.
Respond
Confirmed incidents move through a tracked response timeline — isolate, analyze, verify, report.
Defend against adversaries who don’t stop trying
We're selecting design-partner entities for the first mission-cyber deployment cohort. Book a briefing to review your current ECC/CCC posture.
Request a Pilot