الدفاع والأمن· DEFENCE & SECURITY · DATA GOVERNANCE
Nasijنسيج
One sovereign data fabric, every record cryptographically bound to its classification.
In-Kingdom data lakes with cryptographic separation by classification level, NDMO-aligned governance built in, and a chain-of-custody audit trail on every record from ingestion to disposal.
الثقة تُبنى حين يُعرف مسار كل سجل
“Trust is built when every record’s path is known.”
What Nasij does
Cryptographic classification separation
Secret, top-secret, and restricted data are held in independently keyed enclaves — a breach of one boundary never exposes another.
NDMO-aligned governance by default
Data classification, retention, and ownership policies are enforced structurally, not left to manual labeling discipline.
Per-record chain of custody
Every record carries a signed history — capture, ingest, access, transfer — verifiable independently of the system that produced it.
Dual-approval access control
Cross-classification access and inter-lake transfers require two-person sign-off, logged and immutable.
In-Kingdom hosting, no exceptions
Every data lake, replica, and backup stays within Saudi borders — no foreign cloud dependency at any layer.
Continuous integrity verification
Scheduled hash audits confirm every archived record still matches its origin — tampering surfaces immediately, not at next review.
See Nasij in action
An early UX walkthrough of the product, designed bilingually from day one.
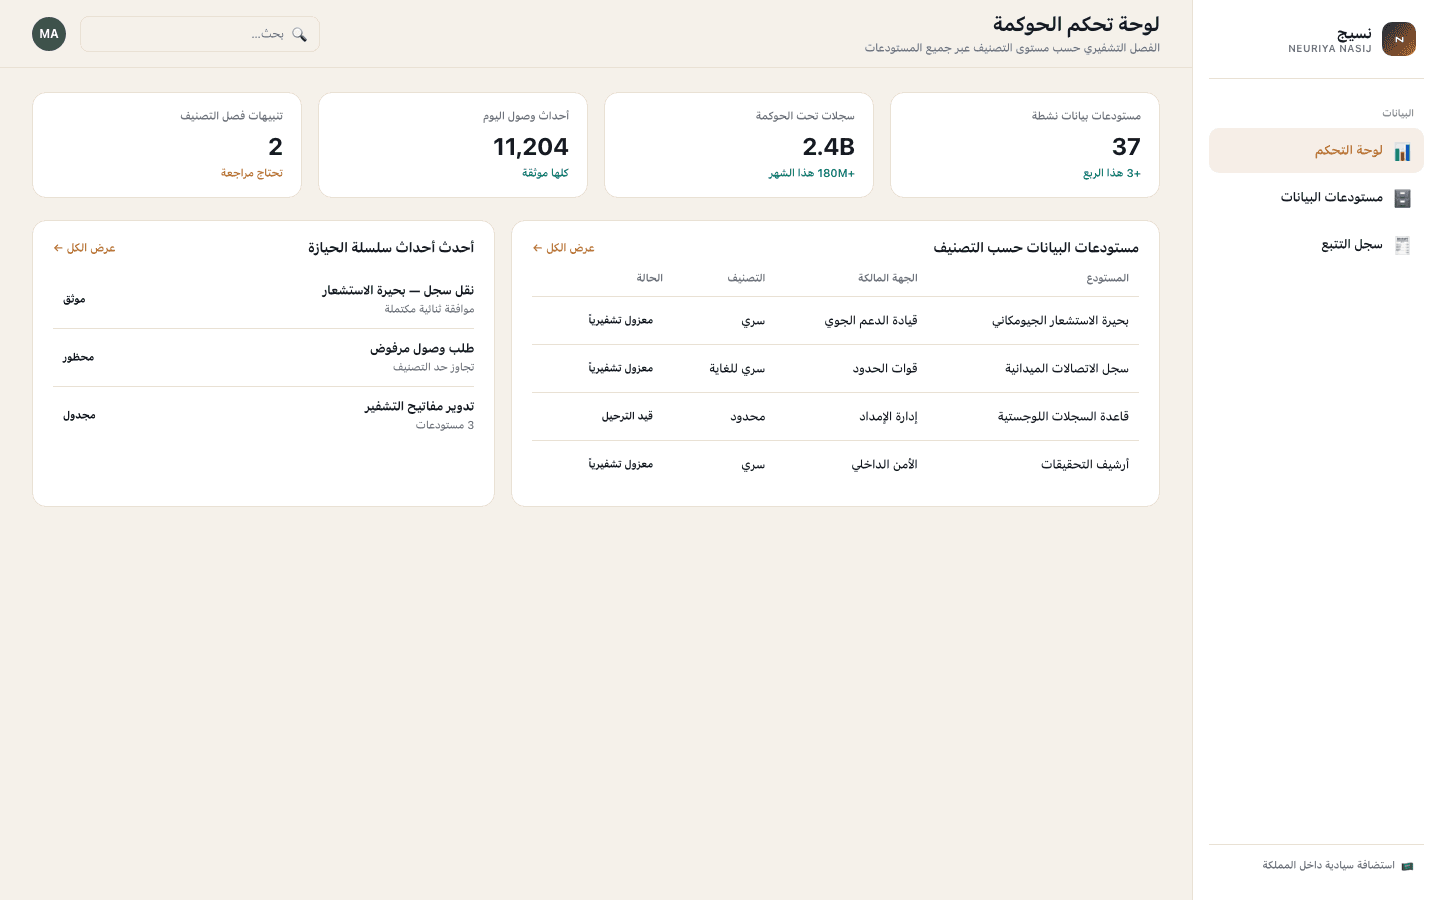
Governance dashboard
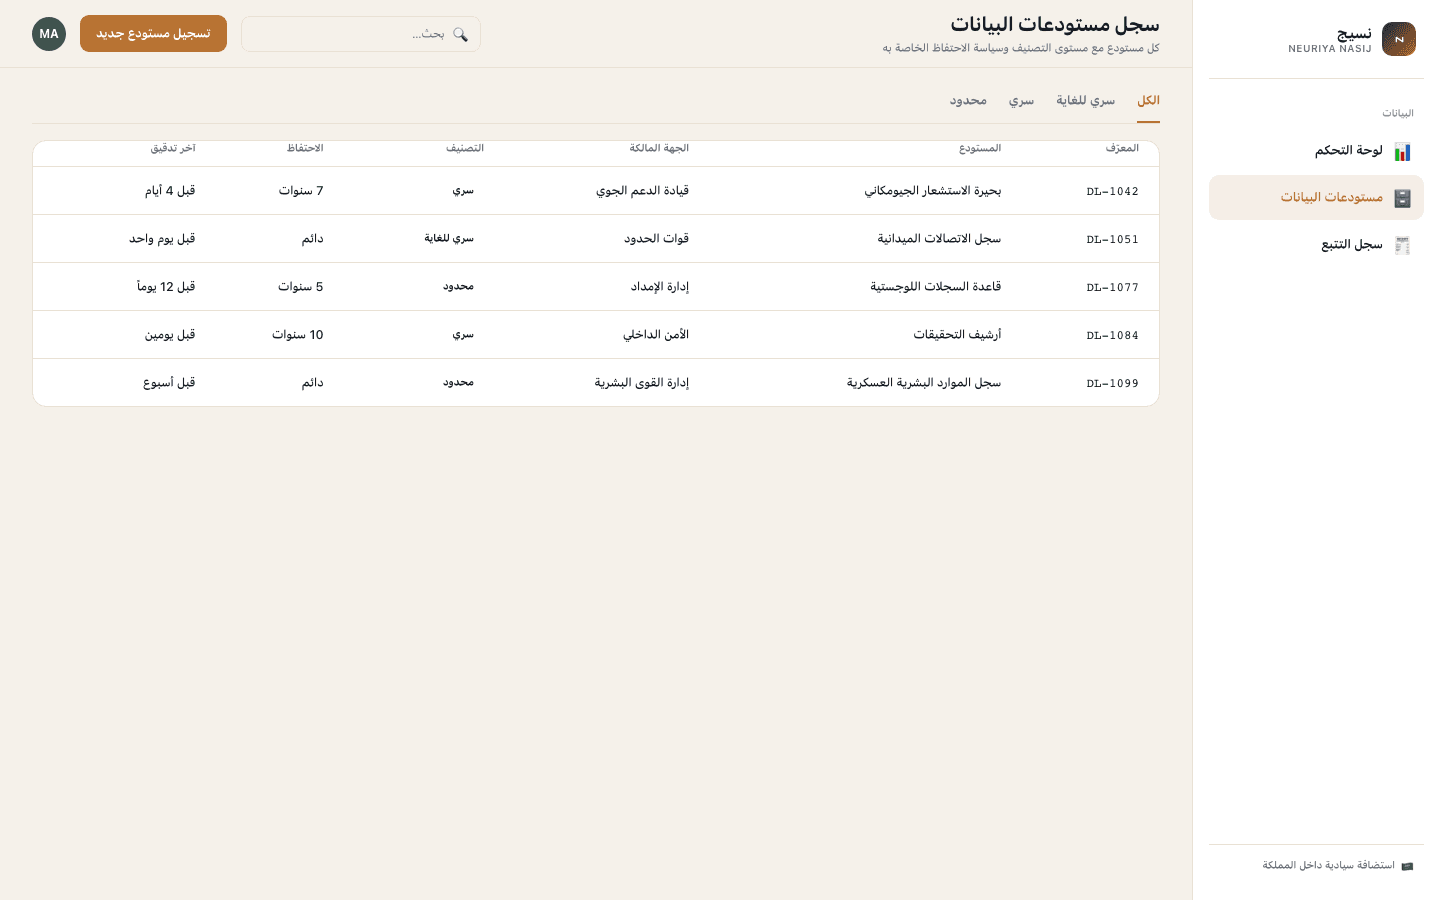
Data lake registry
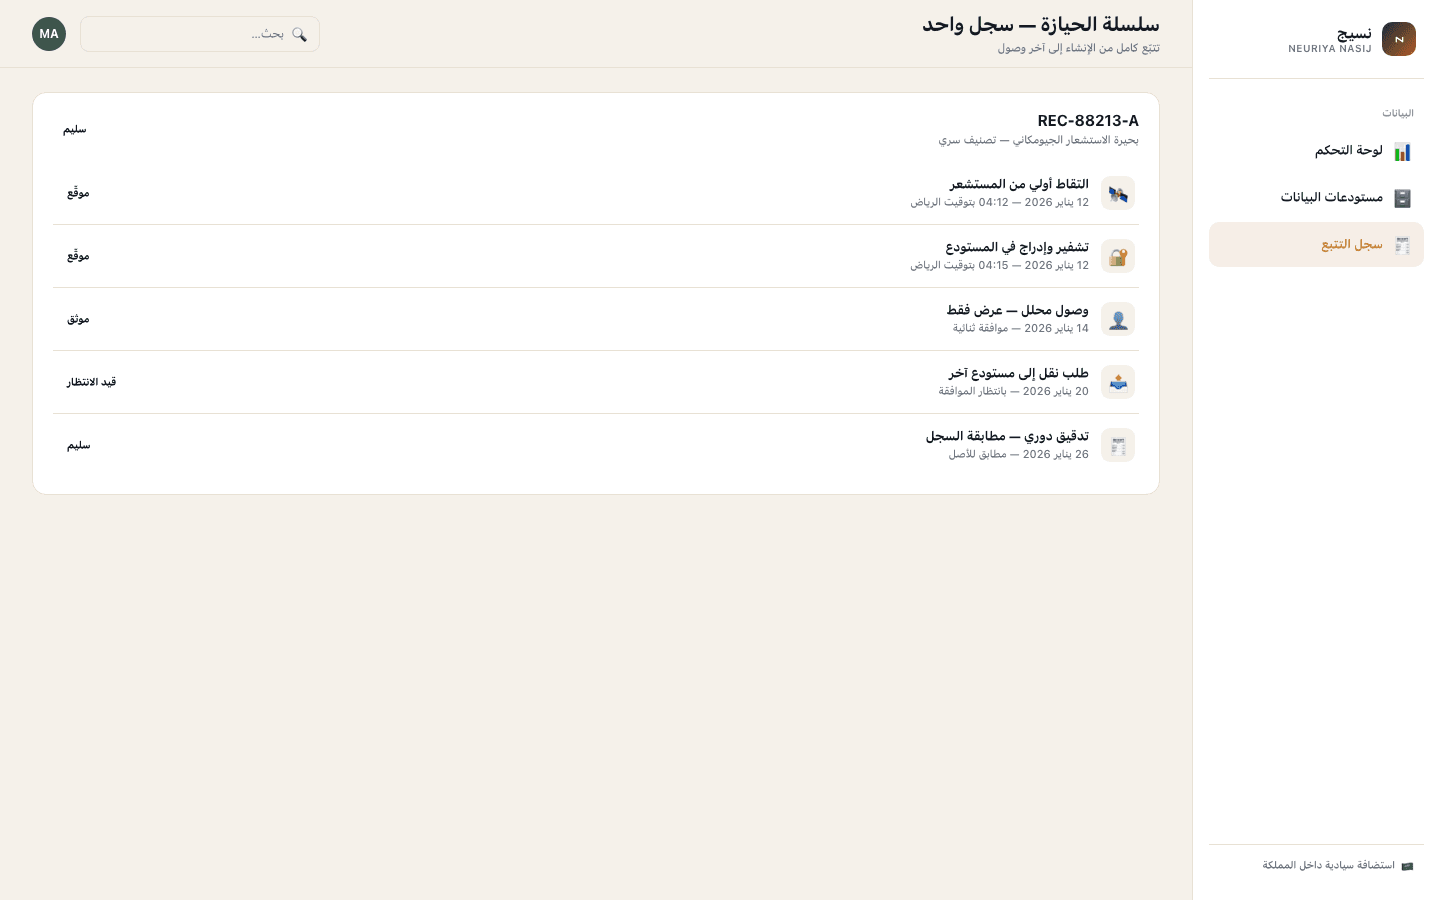
Chain of custody
How it works
Classify
Existing data stores are mapped and classified against NDMO tiers before a single record moves.
Isolate
Each classification tier is provisioned its own cryptographically separated lake, with keys held independently.
Govern
Access, retention, and transfer policies are enforced automatically at the platform layer, not by convention.
Attest
Every access and transfer is logged to an immutable chain of custody, ready for audit at any time.
Bring every classified record under one fabric
We're selecting design-partner defence and security entities for the first accredited deployment cohort. Book a briefing to review fit and accreditation path.
Request a Pilot