Dir'a · Pitch Deck

Defence & Security · CYBER DEFENCE
Dir'aدرع
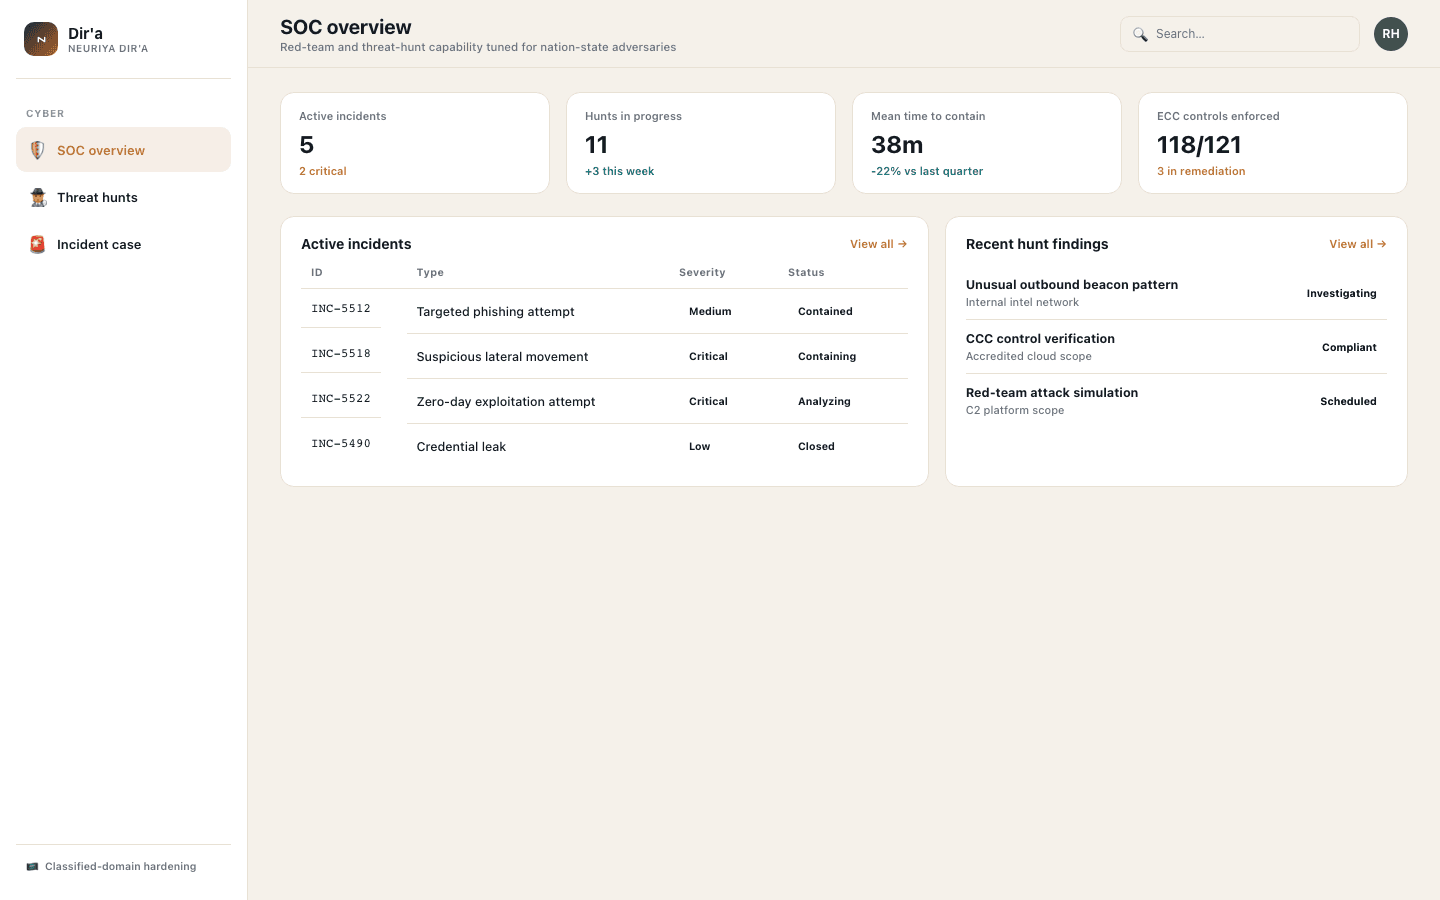
Red-team, threat-hunt, and SOC capability tuned for nation-state adversaries.
neuriya.ai — Sovereign, Arabic-first enterprise AI
Problem
Classified networks are defended with commodity tooling built for commodity threats
- Threat-hunt programs built around commodity malware signatures miss the tradecraft nation-state actors actually use against classified networks.
- Red-team exercises happen infrequently, so defensive posture is assumed to hold between tests rather than continuously validated.
- NCA ECC and CCC control compliance is tracked manually, so remediation status is a periodic report rather than a live picture command can see at any time.
- Detection and response tooling built for commercial networks often needs external telemetry egress, a non-starter inside a classified domain.
Solution
Red-team, threat-hunt, and SOC capability tuned for nation-state adversaries
Product
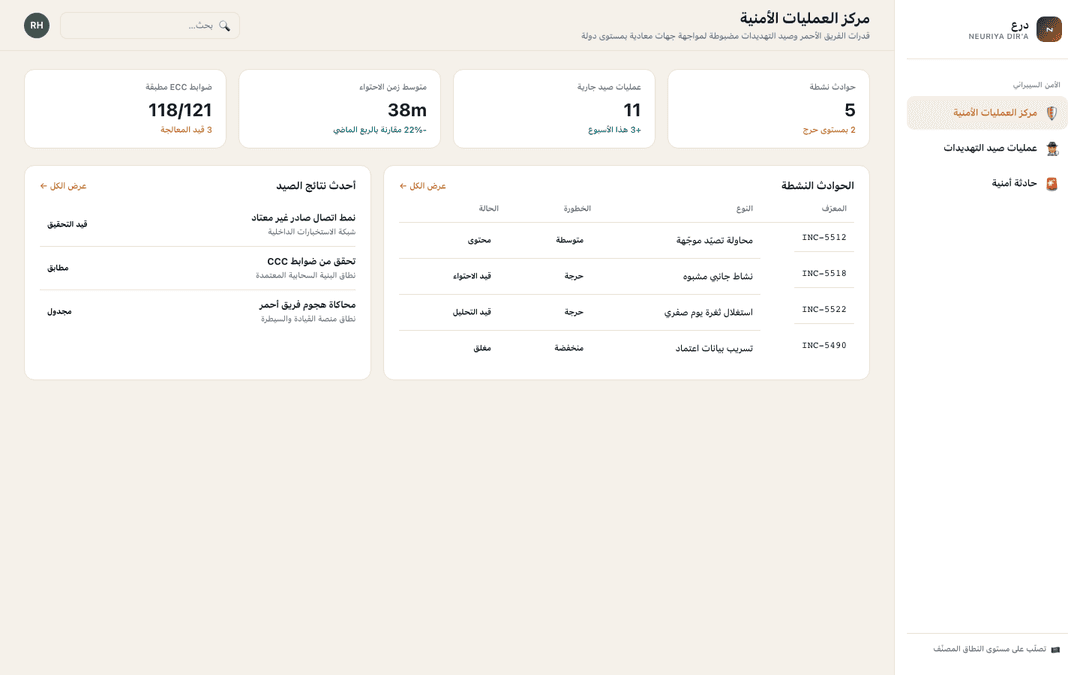
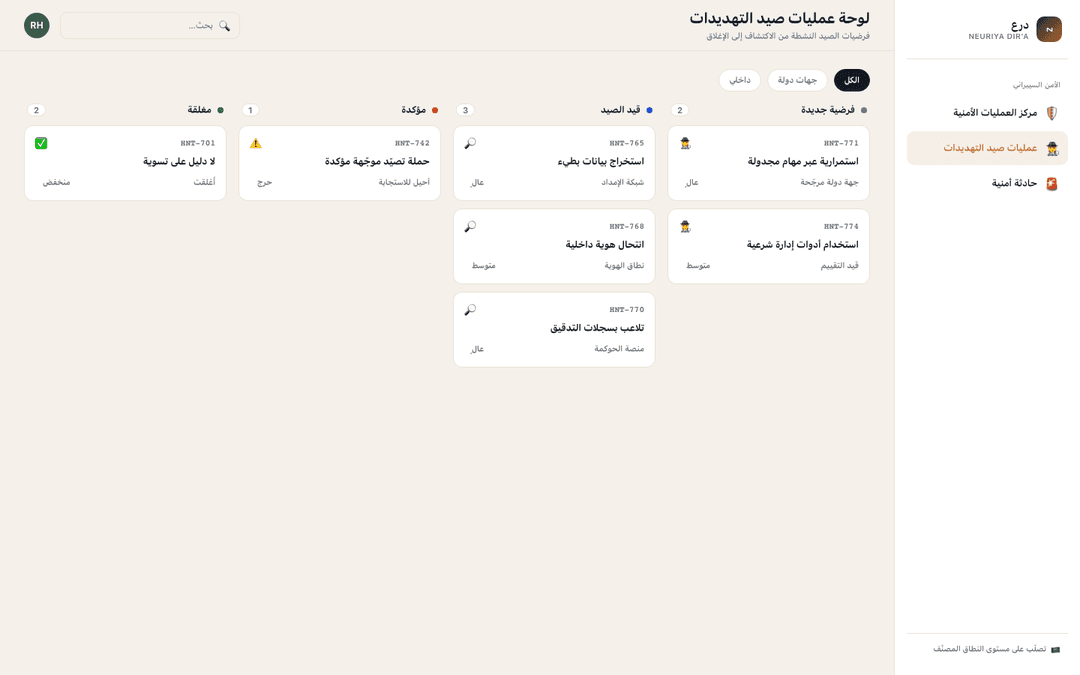
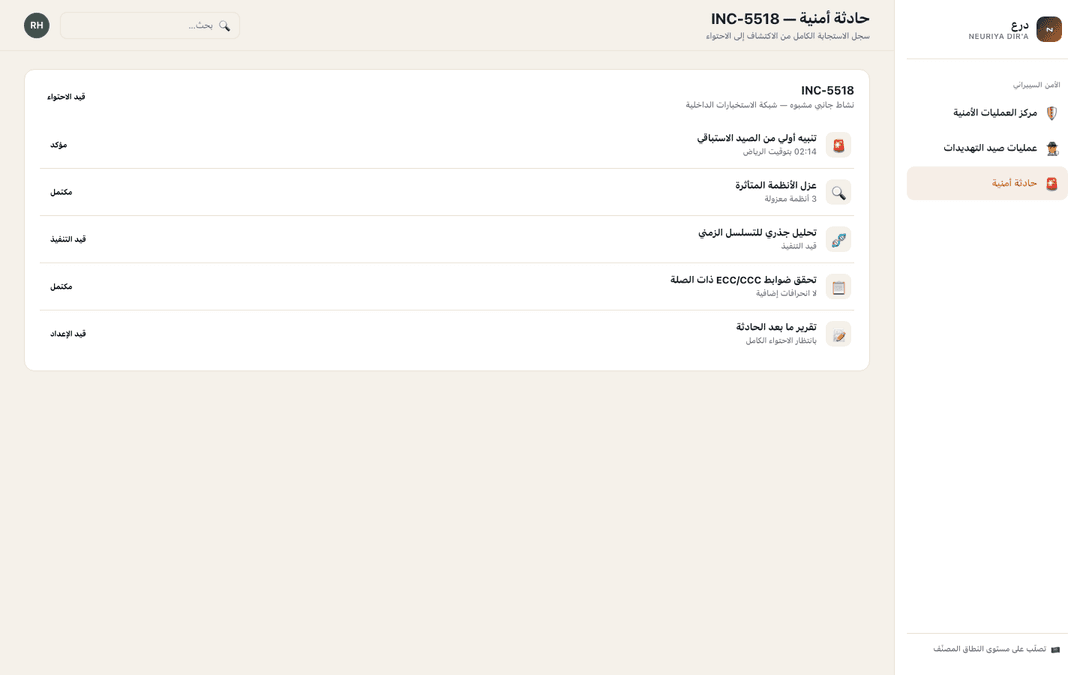
Dir'a in action
How it works
From first touch to outcome
Harden
ECC and CCC controls are baselined and enforced across the classified domain before active defence begins.
Hunt
Threat hunters pursue nation-state-calibrated hypotheses continuously, not only after an alert fires.
Simulate
Scheduled red-team exercises validate that defensive controls hold against realistic adversary tradecraft.
Respond
Confirmed incidents move through a tracked response timeline — isolate, analyze, verify, report.
Market
Sizing the opportunity
- TAM — $2.8B. GCC defence-grade cybersecurity market
- SAM — $350M. Saudi nation-state-calibrated SOC, threat-hunt & red-team spend
- SOM — $24M. 3-year obtainable share via design-partner entity deployments
NCA's tightening ECC and CCC enforcement, combined with rising nation-state cyber activity against Gulf critical infrastructure and defence networks, is pushing entities to replace generic commercial SOC tooling with capability calibrated to that threat level.
Business model
How Dir'a makes money
Per-network SOC subscription
Priced by the number of networks or domains under continuous threat-hunt and SOC coverage.
Scheduled red-team engagement fee
Recurring fee for periodic adversary-simulation exercises against live-representative environments.
Onboarding & control-baseline fee
One-time fee to baseline ECC/CCC controls before active defence begins.
Revenue streams
Where the revenue actually comes from
Competition
Where we win
Our edge
- Hunt hypotheses are calibrated to nation-state tradecraft from day one, not adapted from commodity threat-intel feeds.
- Detection and response tooling is built to run inside classified networks without external telemetry egress, unlike commercial MSSP platforms.
- NCA ECC and CCC control status is tracked continuously, giving command a live posture view rather than a periodic report.
- Founding team combines Saudi defence cyber-operations experience with SOC and threat-hunt engineering.
Traction
Early validation, built for pilot readiness
- Full mission-cyber experience designed and built end-to-end: SOC overview, threat hunt board, and incident case with response timeline.
- Architecture pre-aligned to NCA ECC-2, CCC, NDMO Classification, and ISO 27001.
- Actively selecting design-partner entities for a first mission-cyber pilot cohort.
Go-to-market
Land on one network, expand across the classified domain
- 1Land with 1-2 design-partner entities willing to run continuous threat-hunt and SOC coverage against a first classified network.
- 2Prove mean-time-to-contain and ECC/CCC control-compliance gains over a pilot period against the entity's existing SOC tooling.
- 3Expand to additional networks and scheduled red-team engagements within the same entity, then to further entities.
Team
Built by operators, not just builders
The ask
Raising a seed round to reach first design-partner SOC pilots
We're raising to fund threat-hunt tooling, red-team exercise infrastructure, and the core cyber-operations team through first-revenue pilot deployments.